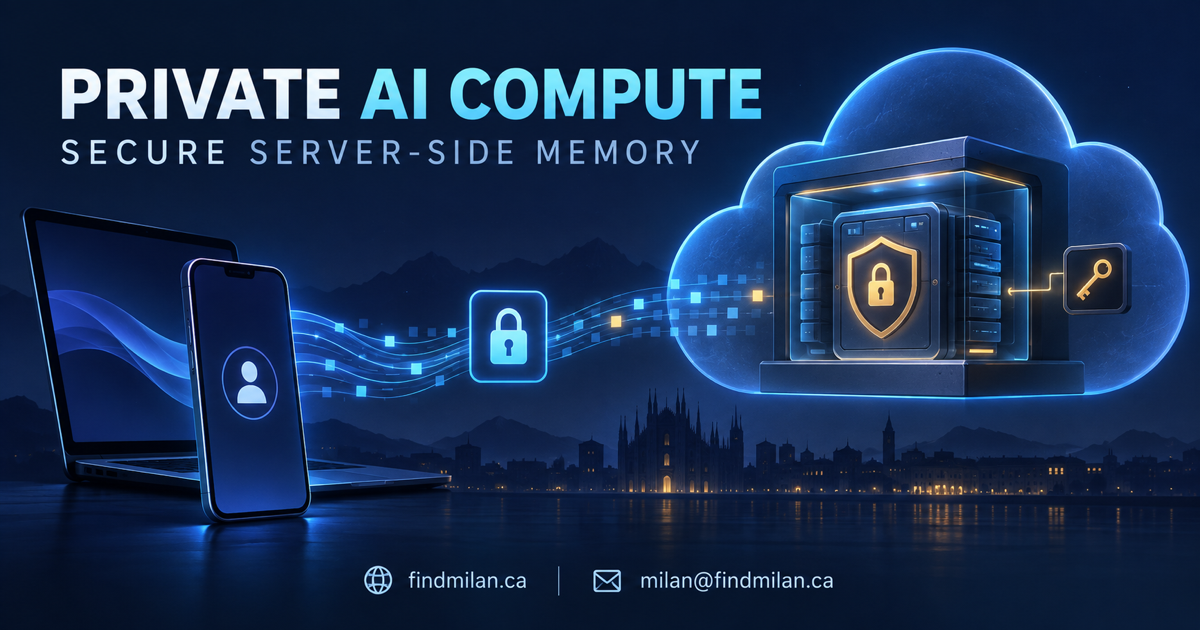
Google’s September 23, 2026 Private AI Compute update describes a planned secure server-side memory layer for AI assistance across devices. The proposal combines hardware-isolated cloud enclaves, encrypted per-user storage, and keys that Google says remain on a person’s devices.
This is an architecture announcement, not confirmation that persistent memory is already broadly available in a consumer product. Google says the design is intended to keep the continuity benefits of server-side AI while protecting stored context; that is a company-stated security goal that still needs to be evaluated against the published technical material and a deployed implementation.
Why server-side AI memory is a different problem
On-device memory can keep personal context close to the user, but advanced models may require more compute than a phone or laptop can provide. Conventional cloud inference can scale, but persistent context creates additional questions about storage, access, retention, and control.
Google’s proposal attempts to combine those properties: retain useful context in the cloud while using device-derived keys and isolated processing so that the service operator should not be able to read the stored information. The design is presented as an update to Google’s existing Private AI Compute platform, which had been described as stateless between tasks.
The architecture Google describes
Google’s blog outlines a flow with four broad steps:
- A device establishes an authenticated, end-to-end encrypted channel to a protected cloud environment.
- A hardware-backed secure enclave receives the information required for the request.
- The enclave temporarily decrypts the relevant context in isolated memory to run the task.
- New context is encrypted into per-user storage, with the necessary cryptographic keys held on the user’s devices.
Google says devices will be able to verify that the server software is authentic and unaltered before sending personal data. The company also says it is publishing a tamper-proof public software record, an updated technical brief, and results from an independent audit. The announcement invites the privacy community to review those materials.
What is announced versus what is available
The post uses future-oriented language: this architecture “will enable” persistent, cross-device memory. It describes the direction and technical design, not a general availability date, supported devices, product settings, or a user migration path. Teams should not assume they can switch this feature on today.
The stated privacy properties are also Google’s claims about a proposed system. A secure enclave and device-held keys can reduce certain access paths, but the exact assurance depends on implementation details such as hardware and firmware trust, remote attestation, key enrollment and recovery, software updates, logging, deletion, and incident response.
Questions to answer before trusting persistent AI memory
When the feature becomes available, users and organizations should be able to determine:
- which conversations or facts are eligible to become memory;
- whether users can inspect, correct, export, or delete stored context;
- how memory follows multiple devices and what happens after a device is lost;
- how device keys are recovered, rotated, or revoked;
- what the independent audit tested, and what it excluded;
- how software transparency records connect to the running enclave;
- how retention, legal requests, and security incidents are handled.
These are evaluation questions, not evidence that the proposed design fails them. They help distinguish a cryptographic architecture claim from the operational controls a real product must provide.
A practical way to read the announcement
The design is notable because it addresses a real tension: AI assistants gain usefulness from continuity, while persistent personal data raises the stakes for privacy and user control. Google’s next step is to make the threat model, technical brief, audit scope, and verification path clear enough for independent review.
FindMilan’s AI consulting service can help teams evaluate privacy, data-flow, and deployment requirements for AI features. The related AI Web Awards project is a separate evaluation product, not part of Google’s Private AI Compute implementation.
Official sources
- Google DeepMind: Advancing Private AI Compute with secure, server-side memory
- Google Private AI Compute technical brief (PDF)
This article separates Google’s description of the intended architecture from practical questions that organizations should verify. The announcement alone is not an independent security certification or proof of product availability.
Frequently asked questions
What did Google announce about Private AI Compute?
Google published a technical update describing a planned server-side memory layer for Private AI Compute. Its proposed design uses hardware-isolated cloud enclaves, encrypted per-user storage, and cryptographic keys held by a user's devices to support persistent context across devices.
Is Private AI Compute server-side memory available now?
The September 23 announcement describes what the architecture will enable and invites review of its technical brief. It does not announce broad user availability, so treat the memory capability as a planned design until Google confirms a product rollout.
How does Google's proposed memory design work?
Google says an authenticated encrypted channel connects a device to an isolated cloud environment. The enclave temporarily decrypts needed information to process a request, saves new context, and encrypts it for storage; device-held keys are intended to control access.
Does Google's announcement prove that the system is completely private?
No. Google describes its intended security properties and says it is publishing software transparency records and independent audit results. Those claims should be assessed against the technical brief, audit scope, attestation process, key recovery design, and deployed product behavior.
What should organizations evaluate before adopting persistent AI memory?
Review what data is stored, how long it persists, how users inspect or delete it, device enrollment and key recovery, enclave attestation, audit scope, incident response, and whether the feature is actually available for the intended product and region.